THE TROJAN HORSE IN A SUIT: THE INTERVIEW WASN'T AS PRIVATE AS YOU THOUGHT.
VigiVend Team
November 4, 2026 · 3 min read
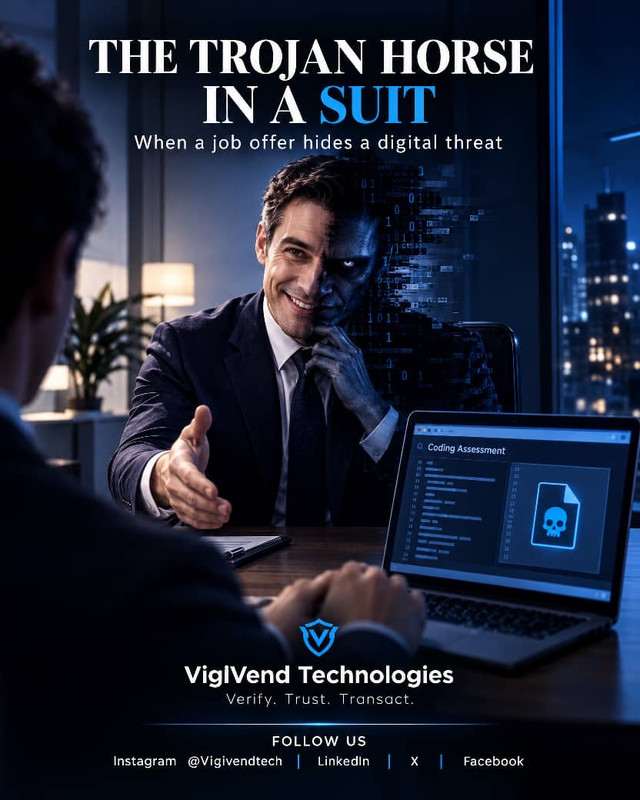
THE TROJAN HORSE IN A SUIT: THE INTERVIEW WASN'T AS PRIVATE AS YOU THOUGHT.
Your CV tells an employer what you can do. But a fake recruiter might be more interested in what your computer can give them.
It sounds like an ordinary recruitment process: a promising job opportunity, a professional conversation and a coding assessment. But what if the person offering you the job isn't interested in your skills at all?
Meet the Trojan Horse in a suit.
In Greek mythology, the Trojan Horse was a seemingly harmless wooden horse used to conceal enemy soldiers who would later attack the city of Troy. Its greatest weapon was deception: the danger was hidden inside something its victims willingly accepted.
Cybercriminals are using a similar strategy, only this time, the disguise is a job opportunity.
HOW THE TRAP WORKS
In an October 6, 2026 advisory, Nigeria's Computer Emergency Response Team (ngCERT) warned about cybercriminals impersonating recruiters on LinkedIn and through email, targeting software developers and engineers.
Their approach follows a calculated pattern:
The Bait: They pose as legitimate recruiters and offer attractive employment opportunities.
The Hook: They invite applicants to complete a coding assessment or review a project file as part of the recruitment process.
The Hidden Threat: Inside the seemingly ordinary project file is malware (malicious software designed to steal information, compromise devices or gain unauthorized access to computer systems).
Once an applicant downloads and executes the infected file, attackers may gain access to passwords, personal files, computer systems and even confidential company source code.
Some of the malware identified in the campaign can function as a Remote Access Trojan (RAT), a type of malicious software that allows attackers to access or control an infected computer remotely.
The applicant thinks they are one step closer to employment. In reality, they may have opened a door to a cyberattack.
AND THERE'S MORE.
On October 24, ngCERT issued another advisory concerning improperly configured email servers.
An open SMTP relay is an email server that allows unauthorized people to send messages through it. Cybercriminals can exploit this weakness to distribute phishing emails, spam and malware.
This means that even the systems businesses rely on to communicate can become tools for cybercriminals when they aren't properly secured.
WHAT CAN YOU DO?
Verify recruiters: Independently visit the employer's official website and confirm that the vacancy exists.
Treat project files with caution: Avoid running unfamiliar coding assignments directly on your primary computer. Developers should inspect untrusted files in isolated environments (separate, controlled spaces that prevent suspicious software from affecting their main systems).
Businesses, secure your email systems: Restrict unauthorized mail relaying and monitor unusual activities.
THE BIGGER LESSON
The Trojan Horse succeeded because its victims trusted what they saw without questioning what was hidden inside.
Cybercriminals understand that people are constantly searching for jobs, scholarships, business opportunities and professional connections. These genuine interests can become opportunities for deception.
At VigiVend, we believe verification should come before trust.
Our WhatsApp verification bot helps users assess unfamiliar links, providing risk assessments for safe, suspicious and malicious links, alongside explanations to guide their decisions.
Because sometimes, the danger isn't in the opportunity itself, but in what comes with it.
Don't let a promising opportunity become an entry point for an attack.
VigiVend — Africa's Trust Gateway.
Verify. Trust. Transact.
Try the VigiVend WhatsApp Verification Bot: https://wa.me/2348055494634
Source: Nigerian Computer Emergency Response Team (ngCERT), October 6 and October 24, 2026 advisories.
Share this article
Discussion
Join the discussion
Loading comments...